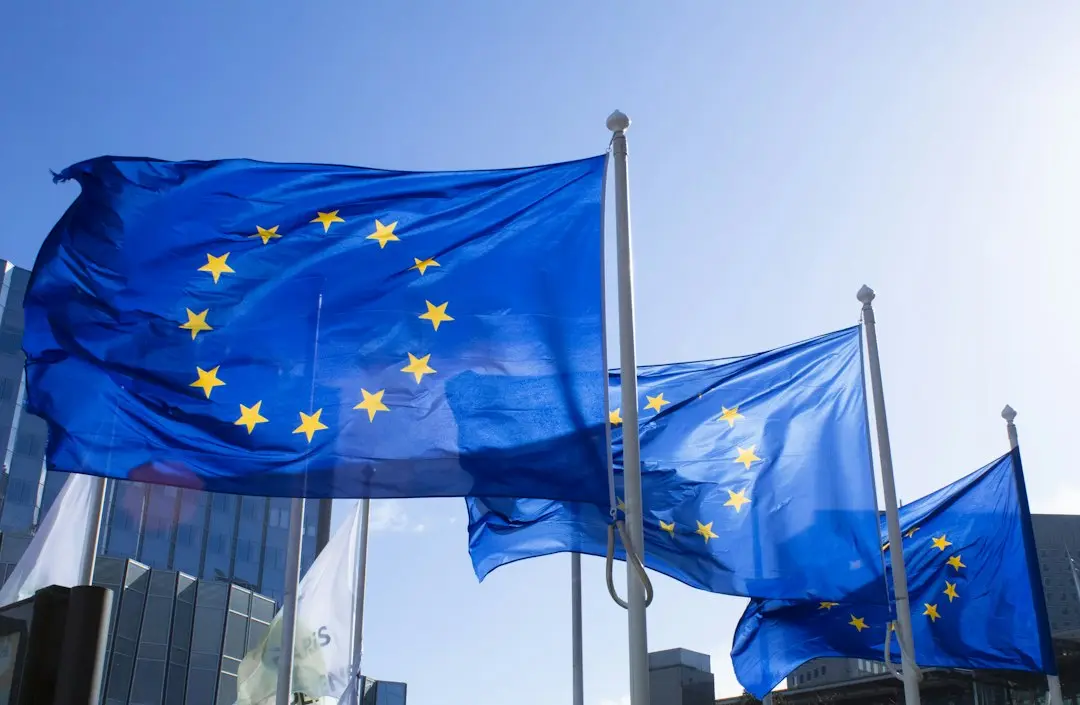
Strengthening Digital Supply Chain Governance
The European Banking Authority has unveiled its final guidelines for managing third-party risks within the financial sector. Released this week, the framework aims to harmonize how banks across the European Union oversee their external service providers. These rules are designed to align directly with the Digital Operational Resilience Act to ensure sector-wide stability.
Breaking news
 X Money Launches with High-Yield Savings and Cashback Rewards
 Splitit Announces White-Label Credit Card Launch
 Billing Friction Puts $12.3 Billion in Auto Loan Payments at Risk
 OneSpan Unveils New e‑Signature Features Including Identity Wallets and AI Workflow Support
The new standards introduce a more proportionate approach to risk management. Regulators want financial institutions to maintain tighter control over their supply chains. This shift addresses growing concerns regarding the reliance on cloud providers and other external technology vendors. By standardizing these governance arrangements, the EBA intends to reduce systemic vulnerabilities across the bloc.
Financial institutions must now conduct more rigorous assessments before signing contracts with third parties. The guidelines require banks to identify potential risks to their core operations early. If a service provider fails, the bank must demonstrate it has a clear exit strategy in place. This ensures that essential services remain functional during a crisis.
How Will These Regulations Alter Daily Banking Operations?
The framework also emphasizes the importance of ongoing monitoring. Banks are expected to audit their partners regularly to ensure compliance with security standards. This proactive stance is intended to prevent operational disruptions that could impact customers. The EBA believes this oversight is critical as banks increasingly outsource sensitive data processing.
Compliance teams will face a significant increase in administrative responsibilities under the new regime. Firms must document every stage of their vendor relationships with greater precision than before. While this adds complexity, it provides a clearer roadmap for managing modern digital infrastructure. Banks that fail to adapt their internal policies risk regulatory penalties and increased operational exposure.
Looking ahead, the industry must prepare for full implementation of these requirements. The EBA expects firms to integrate these practices into their existing risk management frameworks immediately. This transition is essential for maintaining trust in the digital financial ecosystem. As technology evolves, these rules will serve as the primary defense against third-party failures.
Frequently Asked Questions
What is the primary goal of these new EBA guidelines? The guidelines aim to harmonize risk management practices for third-party providers across the EU. They ensure that financial institutions maintain operational resilience while relying on external technology services.
How do these rules interact with the Digital Operational Resilience Act? The new framework is specifically designed to align with the Digital Operational Resilience Act. It provides the practical governance steps necessary to meet the broader requirements set by that legislation.
What must banks do if a third-party service provider fails? Banks are now required to maintain robust exit strategies for every critical service. They must prove they can transition to alternative providers or internal solutions without interrupting essential operations.